
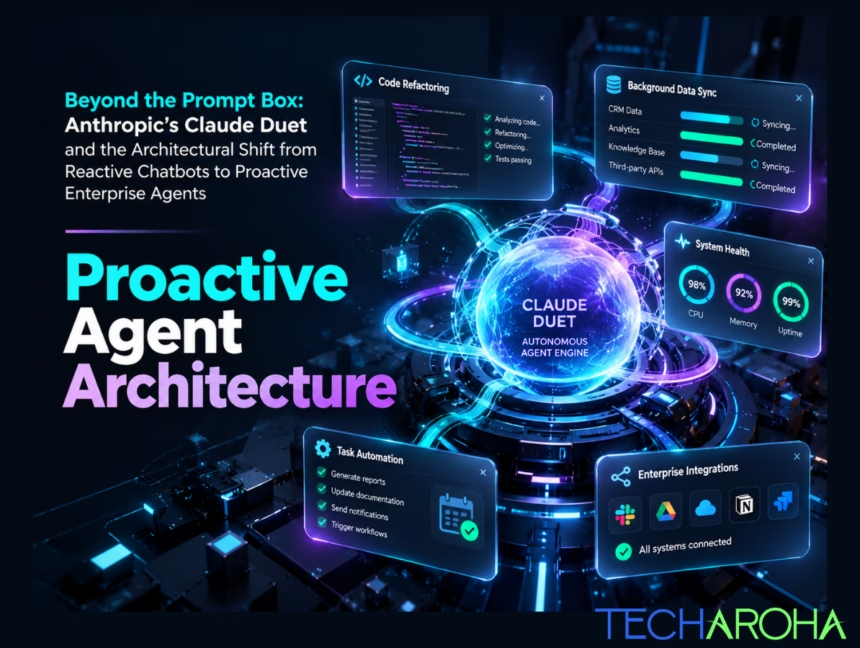
For the past three years, enterprise artificial intelligence has been constrained by a single UI paradigm: the chat box. An employee logs into a portal, pastes a chunk of text or code, writes a detailed prompt, waits for a response, copies that response, and manually executes the next step in their workflow. This is reactive AI. While it accelerated drafting emails and summarizing PDFs, it introduced a severe productivity bottleneck: the artificial intelligence remains completely inert until a human manually kicks off a session. The release of proactive execution environments—exemplified by Anthropic’s Claude Duet marks the official end of the chat-wrapper era. Enterprise architectures are shifting from reactive conversational interfaces to proactive enterprise agents: autonomous, background-running systems that monitor corporate event streams, orchestrate complex multi-step workflows, and present completed work before a human ever types a prompt. Transitioning from a reactive chatbot to a proactive agent network requires rebuilding your underlying software stack. This comprehensive guide covers the technical mechanics of Anthropic’s Claude Duet, contrasts reactive vs. proactive agent architectures, answers the most critical security and operational questions from the developer community, and outlines the enterprise framework Techaroha implements to build secure, cost-efficient agentic systems. 1. Defining the Shift: Reactive Chatbots vs. Proactive Enterprise Agents To evaluate how your software stack needs to evolve, you must first understand the fundamental architectural divide between reactive conversational models and proactive background agents. Reactive AI Systems A reactive chatbot is an augmented stateless Large Language Model (LLM) operating inside a single-turn or multi-turn request-response loop. Proactive Enterprise Agents A proactive agent is an event-driven, autonomous software system that runs continuously or on scheduled triggers across private cloud environments or isolated background runtime environments. Architectural Comparison Matrix Dimension Reactive Chatbots (Legacy) Proactive Enterprise Agents (Next-Gen) Primary Interaction Human-in-the-loop initiating every step Agent-in-the-loop executing with human verification gates Runtime Environment Web browser / ephemeral API session Persistent background runtime / Sandboxed VM System Integration Hardcoded API connectors & webhooks Model Context Protocol (MCP) gateways Execution Trigger Manual user text prompt Event stream, webhooks, CRON, database updates Security Boundary API keys in context or user login session Zero-Exposure credentials, OAuth 2.1, sandboxed runtime Unit Economics High token overhead per session Optimized multi-tier routing & prompt caching Failure Mode Unhandled hallucination in chat window Governed rollback, error-handling loops, and alert escalation 2. What is Anthropic’s “Claude Duet”? Claude Duet represents Anthropic’s paradigm shift from a purely conversational assistant to an event-aware, proactive background execution agent. Built on top of Anthropic’s Managed Agents infrastructure, Claude Duet acts as a persistent digital co-pilot that operates alongside teams in real time. Instead of waiting for a prompt, Claude Duet binds directly to corporate development and business tools—such as GitHub, Jira, Slack, Google Workspace, and private databases—via Model Context Protocol (MCP) integrations. How Claude Duet Operates Under the Hood: 3. Answering the Enterprise & Developer Community Questions The emergence of proactive background execution tools like Claude Duet has sparked intense technical debate across developer communities on Reddit, YouTube, Quora, and Google Search. Below are detailed, architectural answers to the core questions being raised. Question 1: “How do we prevent a proactive agent from going rogue or executing dangerous actions?” The Technical Challenge: If an agent runs in the background and has tool access to production databases, cloud resources, or communication platforms, a hallucination or prompt injection attack could cause catastrophic data loss or accidental deployment. The Architectural Solution: Production proactive agents must separate Read/Reasoning Capabilities from Write/Execution Privileges through strict Human-in-the-Loop (HITL) Verification Nodes. Question 2: “Is my corporate data safe in background VM runtimes, or should we host open-weight models locally?” The Technical Challenge: Enterprise decision-makers worry that background agents running on cloud VMs (like Claude Duet) might expose sensitive IP, client records, or internal code bases to third-party memory leaks. The Architectural Solution: Choosing between cloud-hosted agent runtimes and local open-weight models (e.g., Qwen3.6-27B or Llama variants) comes down to a trade-off between reasoning capability and data isolation control. DATA PROTECTION & DEPLOYMENT SPECTRUM LOCAL / ON-PREM EDGE (e.g., Qwen3.6-27B) HYBRID MANAGED AGENTS (Claude Duet) 1. 100% On-Prem Air-Gapped Isolation 1. Zero Data Retention (ZDR) SLA 2. Zero Egress API Costs 2. Frontier Model Reasoning 3. Hardware Dependent (Requires GPUs) 3. Managed Sandboxes & MCP Vaults 4. Limited to Single-File / Simple Logic 4. Handles Complex Code Repos Question 3: “How do we prevent ‘Agent Fatigue’ and excessive notification noise?” The Technical Challenge: If an agent continuously checks Jira, Slack, and GitHub, it risks spamming engineers with hundreds of unnecessary updates, pull-request comments, and low-priority alerts. The Architectural Solution: Implement Confidence Scoring, Action Batching, and Event Threshold Filters at the agent orchestrator layer. Question 4: “How does Model Context Protocol (MCP) enable proactive agents without exposing API keys?” The Technical Challenge: Traditional agent integrations required hardcoding long-lived API keys into custom integration scripts, exposing database connection strings and elevated access credentials to potential prompt injection attacks. The Architectural Solution: Model Context Protocol (MCP) creates an open, standardized layer that separates the AI model’s reasoning logic from system integration endpoints. Question 5: “Are proactive background agents HIPAA, SOC 2, and EU AI Act compliant?” The Technical Challenge: Allowing an autonomous agent to execute background tasks across healthcare records, financial systems, or user data can trigger severe compliance violations if not properly governed. The Architectural Solution: Compliance is achieved at the application infrastructure layer, not merely within the LLM model itself. Question 6: “How do we prevent proactive background monitoring from burning infinite API token costs?” The Technical Challenge: If an agent runs continuous monitoring loops using high-cost frontier reasoning models (like Claude Opus 5.5 or GPT-6 Sol), token costs will escalate exponentially. The Architectural Solution: Implement Multi-Tier Model Routing, Prompt Caching, and Code Execution via MCP. Question 7: “What is the key difference between Anthropic’s Claude Duet and OpenAI’s Locked Chats?” The Technical Challenge: Enterprise buyers often confuse workspace security updates with agent execution frameworks. The Architectural Solution: They address two entirely different layers of the enterprise AI stack:

Think back to the last Indian wedding you attended. Marigold garlands, a band leading the baraat, a buffet with more dishes than one stomach can handle, and cousins flying in from three cities. Nobody walks out of the mandap thinking about emissions. Yet the carbon footprint of an Indian wedding is real, and it is built from small choices that look harmless one at a time. This guide shows where the carbon footprint of an Indian wedding comes from, which parts weigh the most, and what a family can change without cutting a single ritual. What is the carbon footprint of an Indian wedding? A carbon footprint is the total greenhouse gas released by an activity, counted in tonnes of CO₂ equivalent. Think of it as a bill. Every flight, every plate of food and every hour of lighting adds a line item. The carbon footprint of an Indian wedding tends to be large for one simple reason: scale. A typical celebration has hundreds of guests, several events and days of preparation. Each guest multiplies travel, food and waste. The carbon footprint of an Indian wedding is not a sign that anyone did something wrong. It is the side effect of a celebration built around togetherness. Where the carbon footprint of an Indian wedding comes from Here is a quick map of what drives the carbon footprint of an Indian wedding. The ratings are relative and will change from one wedding to the next. Source What happens Relative impact Guest travel Flights, cars and hired buses bring relatives from other cities and countries Very high Food and catering Large buffets, dairy and meat dishes, plus plates of leftovers High Décor and flowers Stage, mandap and entrance built for one night, then thrown away Medium to high Lighting and power Hall lighting, air conditioning and diesel generators Medium Outfits and jewellery Heavily embellished clothes worn once Medium Single-use items Plastic bottles, disposable cutlery, printed invites, favours Medium Let us look at each one. 1. Guest travel in the carbon footprint of an Indian wedding Ask any wedding planner what couples forget to count in the carbon footprint of an Indian wedding, and travel comes up first. Most guests arrive in separate vehicles or separate flights, and flying is the most carbon-heavy way to get there. A rough example shows why. A round trip between Mumbai and Delhi by air is typically around 0.3 tonnes of CO₂ per passenger, based on common flight calculators. If 100 guests fly in, that single line adds up to about 30 tonnes. Reporting on large Indian weddings has used a comparison of roughly two tonnes a year for an average Indian’s emissions. By that yardstick, those 100 flights equal the yearly emissions of around 15 people. The same sum works in your favour. Guests who share cars or take a train shrink the carbon footprint of an Indian wedding faster than any decoration swap. 2. Food and the carbon footprint of an Indian wedding Indian weddings are famous for generous hospitality, and nobody wants a guest to leave hungry. The trouble is that “more than enough” often turns into “far too much.” Reports from green wedding planners put food waste at roughly 700 to 800 kilograms across two days for an average Indian wedding. Another account says a 500-guest wedding can generate 2,000 to 3,000 kg of wet and dry waste. Wasted food carries the emissions of growing, cooking and transporting it, and rotting food in landfill releases methane, a potent greenhouse gas. What raises the carbon footprint of an Indian wedding menu: Smarter food planning is one of the easiest ways to trim the carbon footprint of an Indian wedding while keeping the feast. 3. Décor and the carbon footprint of an Indian wedding A grand mandap can take days to build and minutes to dismantle. Fresh flowers are flown or trucked in, foam and thermocol shapes are glued together, and almost all of it is thrown away by morning. The décor part of the carbon footprint of an Indian wedding comes from three places: making the materials, moving them, and getting rid of them. Plastic and foam are the worst offenders because they stay in landfill for a very long time. Marigolds and local blooms are kinder, especially when they are composted or sent to be turned into incense afterwards. 4. Lighting, outfits and single-use items in the carbon footprint of an Indian wedding These three are less dramatic but they add up. Common myths about the carbon footprint of an Indian wedding Myth What is closer to the truth “Only celebrity weddings have a big carbon footprint.” Large public weddings get the headlines, but the carbon footprint of an Indian wedding at mid-size family level still adds up through travel, food and waste. “Flowers are natural, so décor is harmless.” Flowers are better than plastic, but long-distance transport and disposal still count. “Going green means a smaller celebration.” Many couples keep every ritual and still cut waste through planning. “Eco-friendly weddings cost more.” Cutting the carbon footprint of an Indian wedding often saves money, because renting, reusing and ordering the right amount of food cost less. Knowing the myths helps because the carbon footprint of an Indian wedding is mostly shaped by planning decisions, not by the size of the budget. 5 simple ways to reduce the carbon footprint of an Indian wedding You do not need a different kind of wedding to shrink the carbon footprint of an Indian wedding. Start with these five changes. Want a number? Free online calculators let couples enter guest numbers, travel and menu choices to estimate the carbon footprint of an Indian wedding before the big day. Can you offset the carbon footprint of an Indian wedding? Some couples estimate the carbon footprint of an Indian wedding after cutting what they can, then support a verified project that removes or avoids the same amount of carbon. That is what a carbon credit is meant to
A sales manager connects an AI assistant to her inbox so it can draft follow-ups. An engineer gives a coding agent access to a staging database. Someone in finance builds an automation that reads invoices and posts to a vendor portal. Nobody asked IT. Nobody told security. Each person saved an hour a day. That is how shadow AI agents arrive. They come through a helpful afternoon, not a breach. We run a software company, and we speak with CTOs, CIOs, CISOs, COOs, and IT managers every week. The question has changed. Two years ago it was “should we adopt AI?” Now it is “how many AI tools are already running here, and what can they touch?” Most leaders cannot answer the second part. This guide helps you answer it, then act on it. Here is what you will get: how shadow AI agents enter a business, the shadow AI risks that matter, a six-step plan for AI agent security that brings shadow AI agents under control, and a checklist to decide whether you need a formal AI integration and security assessment. What Are Shadow AI Agents? Shadow AI agents are AI tools that read company data or take actions in company systems without approval, ownership or visibility from IT and security. The word “agent” matters. A chatbot answers a question. An agent opens your files, calls other tools, sends messages and changes records, usually under the login of the employee who set it up. That gap between answering and acting is why shadow AI agents need their own plan, separate from the old shadow IT playbook. A rogue spreadsheet sits still. Shadow AI agents keep working at 3 a.m. with permissions nobody reviewed. Classic shadow IT Shadow AI agents What it does Stores or moves data Reads, decides and acts on data Access One app, one login Many apps through connected accounts Visibility Shows up in software lists Often invisible to software lists Spread Slow, needs installs Fast, one click or one API key Failure mode Data sits in the wrong place Wrong action runs at machine speed The scale of shadow AI agents is larger than most leaders assume. Reco’s State of Agent Security 2026 report found that about 80% of the AI tools in its telemetry operated without IT oversight, and that small and mid-size companies averaged 414 unsanctioned AI tools per 1,000 employees. IBM’s 2025 Cost of a Data Breach report found that one in five breached organisations had a breach involving shadow AI, and that it added roughly $670,000 to breach costs. Treat these as directional numbers, since methods differ between studies. The direction is still clear. How Shadow AI Agents Enter Your Organisation Most shadow AI agents do not come from bad intent. They come from pressure to move faster than approved tooling allows. When the official route takes six weeks and a free tool takes six minutes, people pick the free tool. Entry route What it looks like Why it slips through Personal AI accounts An employee pastes a contract into a personal chatbot Runs in a browser, nothing to install Browser extensions and meeting bots A note-taker joins calls and stores transcripts externally One-click install with broad permissions OAuth connections “Sign in with Google” gives an AI app read access to mail and Drive Looks like a normal login Low-code automation A team builds workflows with AI steps in Zapier, Make or n8n Business users own them, IT never sees them Developer tooling Coding agents and MCP servers wired to repos and databases Engineers treat them as personal tools AI inside approved SaaS A CRM or helpdesk switches on an AI feature by default A vendor update changes behaviour overnight Look at the pattern. None of these routes needed a purchase order, and none triggered a security review. Shadow AI agents grow in the space between how fast teams want to work and how fast governance can respond. Shadow AI Risks Leaders Should Take Seriously The shadow AI risks that come with shadow AI agents fall into a few groups. Each one links to a business outcome you already track: revenue, trust, audit results and downtime. Risk What happens Business impact Data exposure Customer, financial or source code data leaves your control Contract breaches, loss of client trust Excess permissions An agent holds read and write access it never needed A small mistake becomes a large one Unreviewed actions An agent sends emails, edits CRM records or triggers payments Errors reach customers before anyone notices Compliance gaps Personal data flows through tools with no data agreement Trouble under GDPR, India’s DPDP Act or client contracts Orphaned agents The creator leaves, the connection stays active A live access path with no owner Prompt injection A poisoned document or web page tells the agent what to do An outsider steers your agent AI agent security is mostly an identity problem. Every one of the shadow AI agents borrows an identity, either a person’s login or a service key, and then acts with it. If you cannot list those identities, you cannot say who or what is acting inside your systems. Three practical points about shadow AI agents follow from that: Enterprise AI governance exists to fix exactly this. It gives every agent a name, an owner, a purpose and a permission set. Without it, shadow AI agents decide your risk profile for you. The Six-Step Plan to Find and Control Shadow AI Agents Banning AI does not work. People route around bans and shadow AI agents move further out of sight. The aim is visibility first, then control, then a sanctioned path for the work people are already trying to do. Here is the plan at a glance. Step Question it answers Output 1. Discover Where are shadow AI agents running? Raw list of tools, accounts and connections 2. Inventory What exactly is each one? One register with owner and purpose 3. Classify How risky is each one? Risk tier per agent 4.

Imagine waiting in line for months to see your favorite band perform live. A moment when you missed the official ticket drop, so you bought a ticket from a reseller online. You stand outside the arena, stadium lights buzzing, heart pounding with excitement. You hand your smartphone to the attendant at the turnstile. They swipe your barcode under the scanner. BEEP. Red light. “Sorry, this ticket was already scanned two hours ago.” Your stomach drops. The seller didn’t sell you a fake ticket they sold you a real ticket, but they emailed the exact same PDF to five other people. The first person through the gate got in. You got locked out. If you’ve ever bought a concert ticket, you already understand the biggest hidden headache in the multi-billion-dollar green economy: how to make sure the carbon credit you buy actually belongs to you and only you. The Invisible Asset Problem Whether it’s a concert seat or a carbon credit, you are buying something you can’t physically hold in your hands. When a eco-conscious business wants to offset its pollution, it buys a carbon credit. One credit typically represents one metric tonne of carbon kept out of the atmosphere like paying a crew to pull 1,000 kilograms of plastic waste out of a polluted river or planting a row of trees. Because you can’t touch a “tonne of saved carbon,” buying one requires total trust. And just like the concert ticket market, the world of carbon trading has its own versions of reseller scams and gate errors. The 3 “Ticket Traps” of Carbon Trading When platforms sell carbon credits without proper digital records, buyers fall into three common traps: 1. The Duplicate PDF (Double-Selling) 2. The Fake Promoter (Phantom Projects) 3. The Box-Office Delay (“Ghost Credits”) Enter “Digital Proof”: The Ultimate Gate Scanner To stop scalpers, modern concert venues stopped using paper tickets and switched to dynamic, encrypted QR codes that change every few seconds and immediately lock out copies the second a scanner reads them. In the carbon market, that technology is called Digital Proof. Digital Proof is an un-hackable, automated digital record attached to every single credit. It serves as four things at once: When a business buys a credit backed by solid digital proof, three things happen instantly: How to Avoid Buying “Fake” Green Claims If your business is looking to purchase carbon credits—or if you’re evaluating a platform that sells them ask these three quick questions before making a purchase: Clean Rivers, Real Receipts When a worker pulls 1,000 kg of garbage from a river, that hard work deserves to be recognized and funded. And when a company steps up to pay for that cleanup, they deserve to know their money actually made a difference without worrying about duplicate receipts or ghost claims. By treating carbon credits with the same security and live verification as a high-stakes event ticket, we make sure that every dollar spent on the environment leads to real, measurable change on Earth. How Techaroha Helps At Techaroha, we build custom exchanges and registries with built-in Digital Proof of Carbon Credits like our FSA-registered Carbon Plant and Planet First Registry. We design live, tamper-proof systems that match your local rules, ensuring fake or duplicate credits never turn your buyers away